
Lido: CSM-related vulnerability has been fixed, and the vulnerability was not exploited

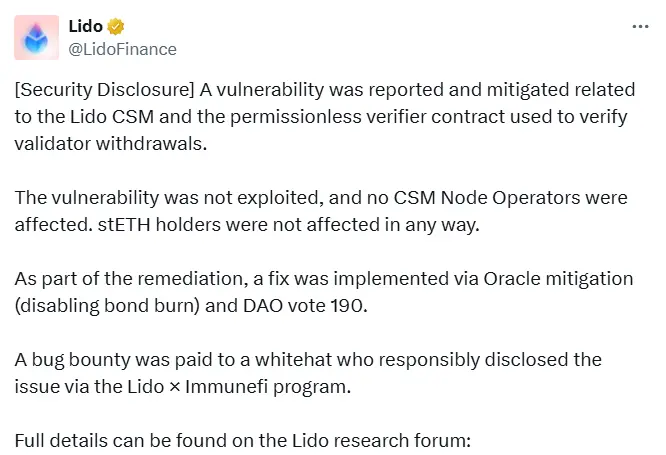
ChainCatcher reports that Lido has published a security disclosure on the X platform: vulnerabilities related to Lido CSM and the permissionless validator contract used to verify validator withdrawals have been reported and fixed.
The vulnerability was not exploited, and no CSM node operators were affected. stETH holders were also not impacted. As part of the remediation, the vulnerability was addressed through an oracle mitigation solution (disabling the bond burning function) and the implementation of DAO Proposal No. 190.
Lido has paid a bug bounty to the white-hat hacker who disclosed the issue through the Lido×Immunefi program.
Disclaimer: The content of this article solely reflects the author's opinion and does not represent the platform in any capacity. This article is not intended to serve as a reference for making investment decisions.
You may also like
Mortgage rates return to 7%, pending home sales in the US fall to nearly a twelve-year low
According to Freddie Mac data, the 30-year fixed mortgage rate has risen to 7.4%, the highest level in nearly three years. Data from real estate brokerage Redfin shows that the volume of existing home pending sales in September fell 4% month-on-month, marking the largest single-month drop in over three years and hitting the lowest level since 2014. Nearly one-fifth of sellers have reduced prices, and the home purchase contract cancellation rate has reached a record high of 14.5%. Inventory levels have risen to the highest since March 2020, but high financing costs continue to constrain transactions.
Mueller Water Products names Michael Morgan CFO, succeeding Melissa Rasmussen
GLD ETF Falls 0.6%
JPMorgan’s tokenized funds on Ethereum hold $844 million
Crypto prices
More


