
Ledger CTO raises alarm over NPM supply chain attack targeting crypto users

A major supply chain attack has rocked the crypto ecosystem, threatening users globally. Ledger’s CTO Charles Guillemet is sounding the alarm, urging caution and hardware wallet use.
- Ledger CTO Charles Guillemet alerts users to a widespread JavaScript supply chain attack silently swapping crypto wallet addresses.
- 18 popular NPM packages were compromised. Libraries like chalk and debug were injected with malware after a developer’s account was hijacked.
- Just $497 stolen so far, but over 2 billion downloads means many dApps and wallets are potentially exposed.
- Protocols like Uniswap, Jupiter, and wallet providers like MetaMask have assured users that their funds are safe.
The attack, which began with a hacked Node Package Manager (NPM) account, has already affected billions of downloads and endangered the security of millions of dApps and crypto transactions.
“The NPM account of a reputable developer has been compromised. The affected packages have already been downloaded over 1 billion times,” Guillemet warned.
He further explained that the malware operates as a crypto clipper, stealthily hijacking wallet addresses during transactions to redirect funds to the attacker’s wallets. Guillemet urged users to be extra cautious, especially those not using hardware wallets.
“If you use a hardware wallet, pay attention to every transaction before signing and you’re safe. If you don’t, refrain from making any on-chain transactions for now,” he advised.
NPM hack: How the breach happened
Reports revealed that 18 popular NPM packages were found to be compromised, including high-profile packages such as ‘chalk’, ‘debug’, and ‘strip-ansi.’ The attack, which happened on Sept 8, is among the largest in recent history, impacting libraries with a total of more than 2 billion weekly downloads.
The attack allegedly began with a phishing email impersonating official NPM support. The target was Qix-, a respected developer whose NPM account was hijacked, enabling attackers to inject malicious updates into popular JavaScript libraries.
Once installed, the malicious payload silently replaces copied crypto addresses with lookalike ones controlled by the hacker. This technique, powered by Levenshtein distance logic, tricks unsuspecting users into sending funds to the wrong addresses.
One main wallet address linked to the attack was highlighted by researchers, though they flagged additional wallets believed to be connected.
Although Charles said it is not clear whether the attacker is also stealing seeds of software wallets at this point directly, recent reports have shed light on the damage. Researcher Rani Haddad categorized the wallets of the attacker on Arkham as an entity called NPM attack. The data indicates that the attacker was able to steal $497.96 at press time.
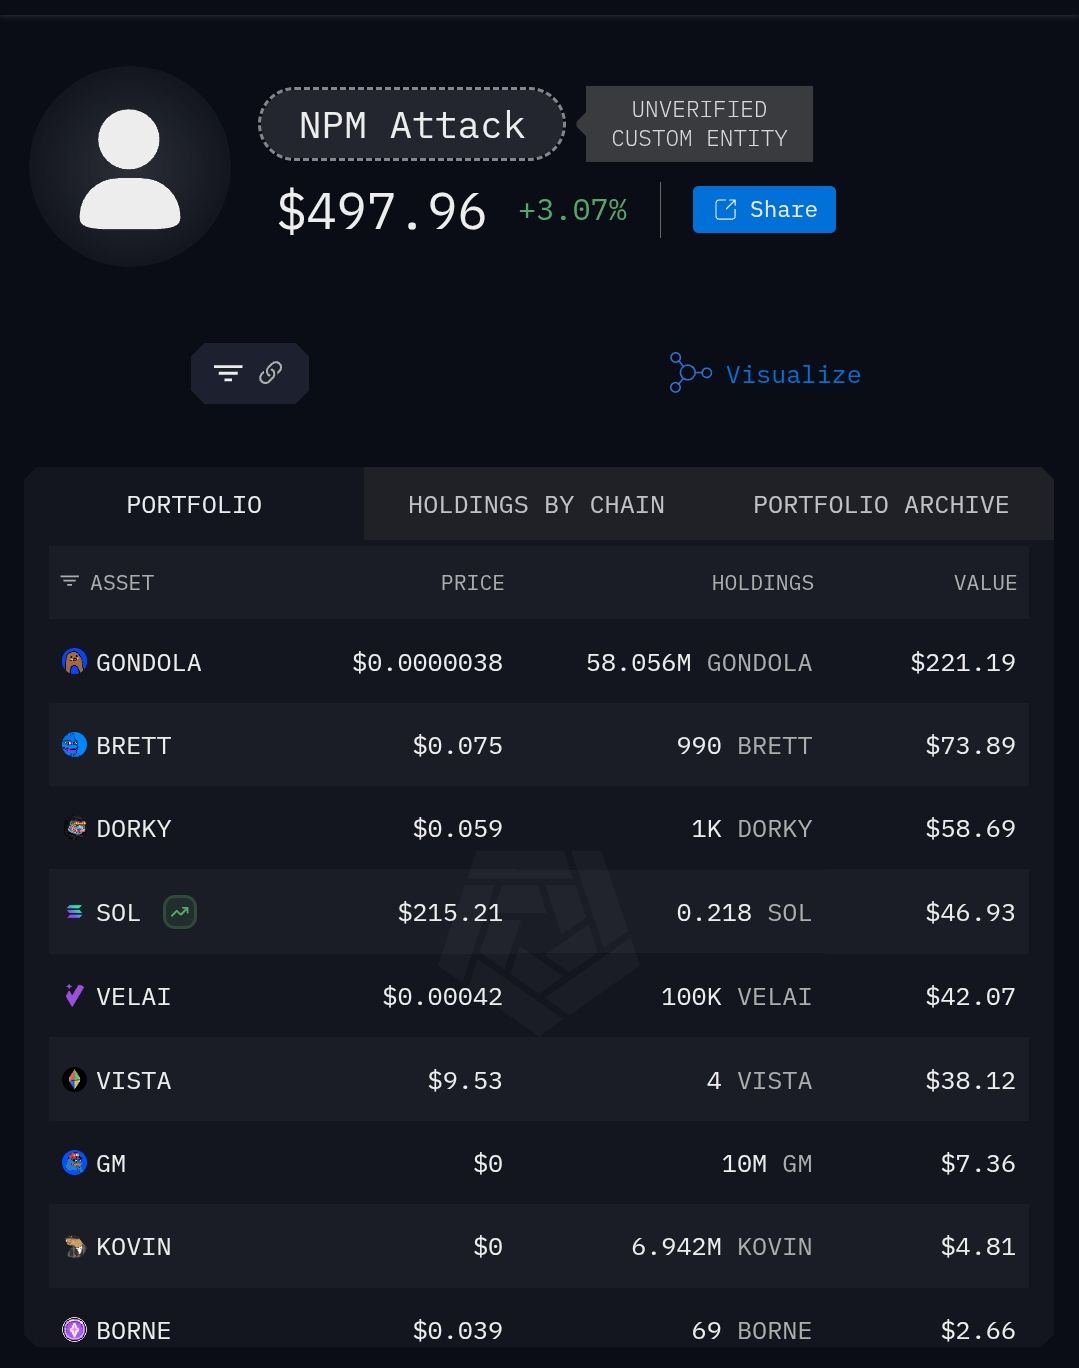 The wallets of the attacker | Source: Arkham
Although the direct financial effect is not that significant, the possible magnitude is immense considering the popularity of the affected packages.
Community response and prevention
A number of projects and protocols, such as Uniswap, SUI, and Jupiter, have affirmed that they are not affected but have advised caution. Cryptocurrency wallets such as Ledger and MetaMask assured users of multi-layered security measures.
Meanwhile, the NPM supply chain hack was not the only major security event on Sept. 8. Swiss crypto wealth platform SwissBorg reported a $41 million exploit via a partner API, affecting 1% of users. Additionally, the Ethereum L2 project Kinto announced its shutdown after a July exploit drained 577 ETH, leaving the team unable to secure funding.
This wave of attacks is an indicator of the increasing complexity of crypto threats. Going forward, users, developers, and platforms need to embrace more secure practices and rigorous package audits.
Disclaimer: The content of this article solely reflects the author's opinion and does not represent the platform in any capacity. This article is not intended to serve as a reference for making investment decisions.
You may also like
Australia Unemployment Rate set to remain at a five-year high of 4.6% in September
Blackstone's AirTrunk Postpones $1.5 Billion REIT IPO: Yield Raised to 6% but No Takers, AI Infrastructure Financing Faces 5.2% US Treasury Yield
AirTrunk, a data center operator under Blackstone, has decided to postpone the listing of its $1.5 billion Singapore Real Estate Investment Trust (REIT) to the first or second quarter of 2027. Rising U.S. Treasury yields and increased market volatility have made investors more cautious; even raising the yield from 5.5% to around 6% has not boosted demand. High capital costs are becoming a major constraint on the expansion of AI infrastructure.
CoreWeave Faces Dual Shock in Stocks and Bonds! Share Price Plummets 15%, Bonds in Trouble, Musk Exclaims "Scary"
Analysts point out that the company borrows at an interest rate of about 9%, but its investment returns are less than 5%. With total debt and lease obligations amounting to $52 billion, there is a risk that its equity value could go to zero. Rising inflation has pushed up long-term U.S. Treasury yields, leading to systemic doubts about the financing logic of capital-intensive AI companies. Prediction platforms now estimate the company's probability of bankruptcy before 2027 at 17%.

Federal Reserve Beige Book Warns of "Fierce" Oil Prices: Half of Districts Face Strong or Intensifying Price Pressures, Businesses Confront Price Increases and Profit Squeeze
The Beige Book shows that all 12 Federal Reserve districts reported the impact of rising oil prices. Businesses generally indicated that high diesel prices and fuel surcharges are passing additional costs down the entire supply chain. Since the previous Beige Book report just over a month ago, the U.S. economy has experienced moderate growth, with manufacturing serving as the main support. The labor market continues to see low hiring and low layoffs, and firms in nearly half the districts reported that AI investment is impacting employment.
Crypto prices
More


